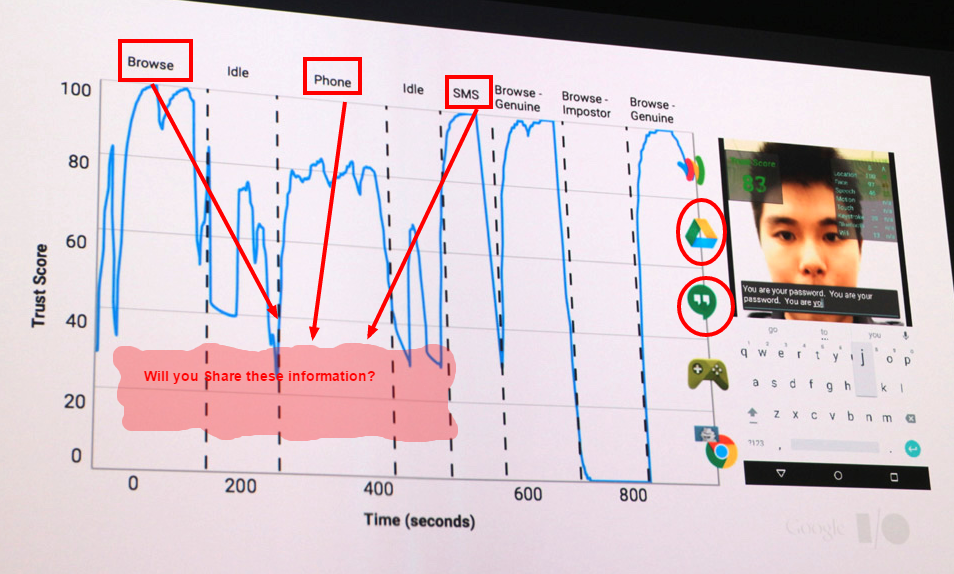
Passwords have become an integral part of our lives (though it’s always tough to remember the right one at the right time). Can you imagine your present life without using any passwords? No! But Google thinks you can! This is what Google has in store for us in 2016- Project Abacus. This project in the most crude of languages means killing our age old beloved ‘password’ and replacing it with smartphone user authentication via a collection of biometric readings that cant actually be cracked easily. What’s more? Abacus will be developed in such a way that it would lock or unlock devices and apps based on a criterion called ‘trust score’ which will increase as your phone continually monitors and recognizes your location patterns, voice and speech patterns, how you walk and type, and your face.
The proponents of this Project are joyous as they believe that this is the most secure and miraculous way of securing your device as compared to the two-factor authentication as in the latter case, the whole system crashes if you lose the access to SMS. During its first public demo at Google’s I/O conference, Regina Dugan claimed that with its “trust score” method, Project Abacus “may prove to be ten-fold more secure than just a fingerprint sensor.” And it’s easy to believe this could be true.
The idea though new and interesting isn’t inviting much of appreciation from the opponents. For example Cisco Engineer Shawn Cooley countered the Project by saying : “very cool until I break my leg or hand & can’t auth to any services to get healthcare info since my behaviour is different.” To this, there is more because according to Google experts, the smartphone will know about your health and your present state of mind with the help of all the data and constant monitoring. So Google actually tracks and records almost everything and anything related to you. So in order to present you with that perfect security, Google will require a constant invasive surveillance and access to some pretty intimate records of the people involved. Sounds exciting? Not anymore!
The two-factor authentication is currently trending which combines login with a text message or email you need as a second step for verifying it’s really you. It’s tougher to hack, and this year it’s being phased in for banking customers by federal mandate. Apart from this, there is also the fingerprint method but what if it is obtained by force? So a way to discover more secure ways is on.
Apart from securing your account, doesn’t it occur to you that securing Android (the most hacked OS) should be the first step in this direction? And God knows, how comfortable would people feel about an app collecting almost all the sensitive information about them to build and present a ‘trust score’ just so that they can log in safely into their emails, etc.
As much as we try to convince ourselves that what Google is doing is actually for our benefits, but will it still be foolproof considering the data collection on us has gone way too far and the data collection sites are the ones struggling with their security. There is a lot to be done in this field. Security of everything around the user has to be perfect and foolproof.
[adinserter block=”7″]
Author: Technology Blog

